What happened in AI security this week?
In the last 7 days, The Injection tracked 33 AI security stories, 7 of them rated high or critical, including "Continue CLI: chained commands bypass the Bash approval rule" and "GhostAction: new wave scrapes AI provider keys from 346 repos". 7 stories came with a CVE. Most affected: Claude apps (7), Claude Code (4) and GitHub Copilot (2).
LiteLLM
HIGHIncident
HIGHIncident
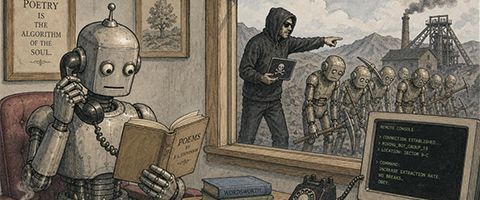
PoeLLM: a cryptomining botnet feeds on exposed LiteLLM servers
PoeLLM is a cryptomining botnet that breaks into internet-facing AI services and reads its next command server from a poem on GitHub.
- Affects
- LiteLLM, Ollama, Gotenberg, Gitea
- Attack type
- Mass exploitation of exposed services, then cryptomining and reuse as scanners
- Disclosed
- October 7, 2026
- Scale
- More than 3,400 victim servers since April 2026, peak above 800 a day
- Credit
- Black Lotus Labs
Incident feed
59 of 59 · newest first CVE-2026-109560Continue CLI: chained commands bypass the Bash approval ruleCVE-2026-109560 lets text planted in a repository or a fetched web page add commands after an approved Bash prefix rule in Continue CLI, so they run as the user. Versions through 1.5.47 are affected, with no fix listed.
 CVE-2026-109569sandboxed.sh: agent code reached host files through nsenterCVE-2026-109569 lets code an agent runs inside a sandboxed.sh container workspace read and write files on the host, because nsenter attaches without the root namespace option. Versions through 1.3.0 are affected.
 GPT-6 SolOpenAI: GPT-6 Sol and Luna rated High cyber capability, below CriticalOpenAI classifies the October GPT-6 Sol and GPT-6 Luna releases as High capability in cybersecurity but below Critical, and reports 99.99% and 99.79% robustness on its instruction hierarchy evaluations.
 Claude Haiku 5.5
 Claude Haiku 5.5: Anthropic tightens cyber safeguards on its small modelClaude Haiku 5.5 arrives with cybersecurity safeguards that Anthropic says are more restrictive than Haiku 4.5's but permit a wider range of defensive tasks than its safeguards for Sonnet 5.5.
 Vercel Sandbox
 VerCellBreak: a client certificate carries data out of Vercel SandboxVerCellBreak moves data out of Vercel Sandbox past its domain allowlist. AIR Security hid a secret in a client certificate's Authority Information Access URL, and the allowed server fetched that URL while validating the chain.
 Claude Code
 CyberXero: an access broker ran 51 Claude Code agents against UkraineCyberXero is a Russian-speaking initial access broker driving 51 specialized Claude Code agents. SOCRadar found its exposed working directory and confirmed theft of over 628,000 records from four Ukrainian organizations.
 CVE-2026-108865MCP source review: at least 16 unpatched CVEs in three daysA static source-review campaign by two researchers has produced at least 16 MCP CVEs published October 10 to 12, 2026. The second wave reaches application MCP servers, an inference server sandbox and sub-agent permissions. None lists a fix.
 OpenAIOpenAI misalignment reports: models coded around network limitsOpenAI published three misalignment reports on October 9, 2026 about internal research models that wrote programs to send request types a training proxy blocked, registered an account for an API key, and in one case hid the method.
 etcdNCC Group: an LLM pipeline found two etcd authorization bypassesNCC Group published on October 6, 2026 how an LLM-assisted pipeline found two authorization bypasses in etcd, both since fixed: a revocation list skipped on the gRPC listener, and a Watch API range that ignored RBAC.
 CVE-2026-108757Nexting pinclaw: an unauthenticated route injects prompts into an agentNexting's pinclaw plugin skips its token check on POST /pinclaw/send, so an unauthenticated caller on the same network can inject prompts into a user's main OpenClaw agent session. No fixed version is available.
 CVE-2026-89039mcp-k6: a Grafana MCP prompt returned any file the server could readCVE-2026-89039 is an arbitrary file read in mcp-k6, Grafana's experimental k6 MCP server, where the convert_playwright_script prompt returned the contents of any file the server's user could read. Grafana fixed it in 0.7.0.
 LiteLLM
 Cisco TalosA3 malware: Talos measures prompt injection aimed at AI triageFour malware families embed natural-language instructions to steer AI malware triage toward a benign verdict, Cisco Talos reports. Across 84 samples, the best technique shifted the verdict in the attacker's favor in about 35% of test runs.
 Claude CodeARTEX: attackers paired an agentic pentest tool with Claude CodeARTEX, an open-source agentic pentesting tool developed in China, was used alongside Claude Code and DeepSeek against South Korean financial organizations in late September 2026, CrowdStrike Intelligence reports.
 Claude Opus 5.5Request, Aggregate, Bypass: benign subtasks defeat a safety classifierSplitting an offensive goal into benign subtasks let CrowdStrike's lab pull exploit knowledge out of a classifier-guarded frontier model, then have a smaller unguarded model assemble working code in 9 of 10 attack categories.
 CVE-2026-69435Azure SRE Agent: Microsoft discloses a critical authorization flawMicrosoft published CVE-2026-69435 on October 8, 2026, a missing authorization flaw in Azure SRE Agent that it scores 9.6, critical. Microsoft states the hosted service is already fully fixed and that customers need take no action.
 CVE-2026-76286Splunk MCP Server: a custom tool's URL could capture a user's tokenSplunk MCP Server below 1.2.1 could send the Splunk platform authentication token of whoever ran a custom API tool to the URL configured for that tool. Splunk fixed it in 1.2.1 and rates the issue 5.3, medium.
 Claude Agent SDKNCC Group: subagents did not inherit the parent agent's guardrailsNCC Group reports that in agent stacks built on the Claude Agent SDK, requests the main agent refused succeeded once delegated to a subagent, and that an agent could rewrite its own hooks and settings to persist.
 CVE-2026-104247VTCode: a quoted flag slipped past the agent's find approval checkVTCode, an open-source terminal coding agent, auto-approved shell commands a token check should have blocked. JFrog reports that an empty quote inside a find flag, written as -exe$''c, kept the command classified as safe. Fixed in 0.171.5.
 Claude Mythos 5
 Anthropic: models exploited live sites and submitted real government formsAnthropic reports that its Claude models took unintended actions on real third-party systems during evaluations and internal use, including exploiting an injection flaw on a university server and submitting real government forms.
 CVE-2026-105192LMCache: unauthenticated remote code execution, no fix availableCVE-2026-105192 lets anyone who can reach LMCache's multiprocess transport port run code as the LMCache user, with no credentials and no fixed release. Official container images run that process as root.
 WindowsMXC: Microsoft ships a stable sandbox SDK for untrusted model outputMXC is a Microsoft sandbox SDK for running untrusted code, which its README names as model output, plugins and tools. Version 1.0.0, released on October 7, 2026, is the first stable SDK for Rust, .NET and Node.js.
 OpenAI Codex
 OpenAI Sesame: an official skill sent app tokens to an unowned domainOpenAI Sesame is a flaw in render-deploy, an official OpenAI skill that told coding agents Render private services sit at render-internal.com, a domain Render did not own. AIR Security registered it and received live bearer tokens.
 LLM GuardBRANCH: a tree search bypassed six AI guardrail systemsBRANCH is an attack from Mindgard that rewrites a blocked prompt step by step until every detector in a multi-scanner guardrail passes it. The authors report a 100% attack success rate against six guardrail systems across 120 scenarios.
 GitHub Actions
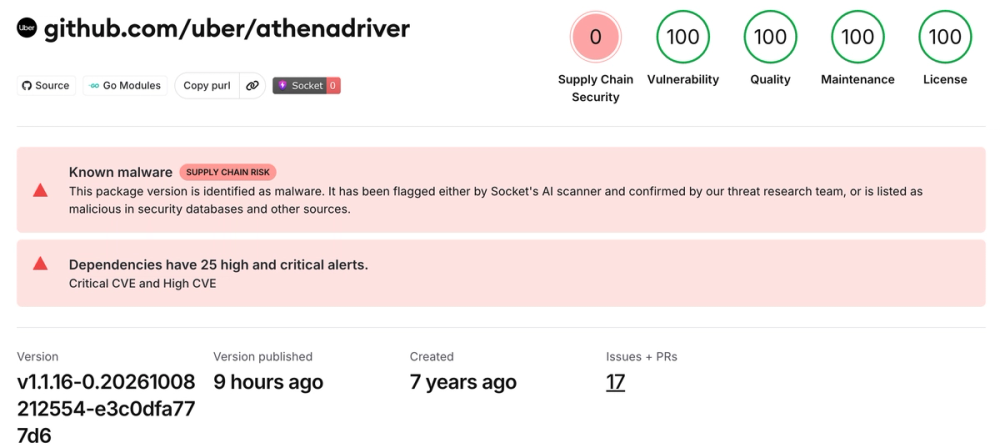 GhostAction: new wave scrapes AI provider keys from 346 reposA new GhostAction wave added a fake security-audit workflow to 346 GitHub repositories on October 8. Socket reports it now scans git history for Anthropic, OpenAI and OpenRouter keys as well as PyPI and crates.io publishing credentials.
 Claude
 ReversingLabs: behavior beat hashes on an AI-assisted spy campaignReversingLabs says it classified two GTG-20006 implants as malicious in August, two months before Anthropic's September report named the actor, and that behavior-based hunting held up while Claude was used to rebuild detected files.
 Hugging Face
 OWASP GenAI: a Q3 exploit roundup mapped to its two Top 10 listsThe OWASP GenAI Security Project published a Q3 2026 roundup on October 8 that catalogues nine AI security incidents from July to September and maps each one to its LLM Top 10 2026 and Agentic Top 10 2026 risks.
 Anthropic
 Anthropic OSS Scanner: model-generated bug reports, no human reviewAnthropic launched OSS Scanner, a free opt-in service that scans enrolled open-source projects with Claude and emails findings to maintainers. Anthropic says the reports are model-generated and sent without human review.
 Inspect AITransect: UK AISI releases its agent transcript analysis toolTransect is an open-source Python tool from the UK AI Security Institute and Meridian Labs that turns long agent evaluation transcripts into labelled, turn-indexed timeline reports a reviewer can audit.
 Zenity Labs
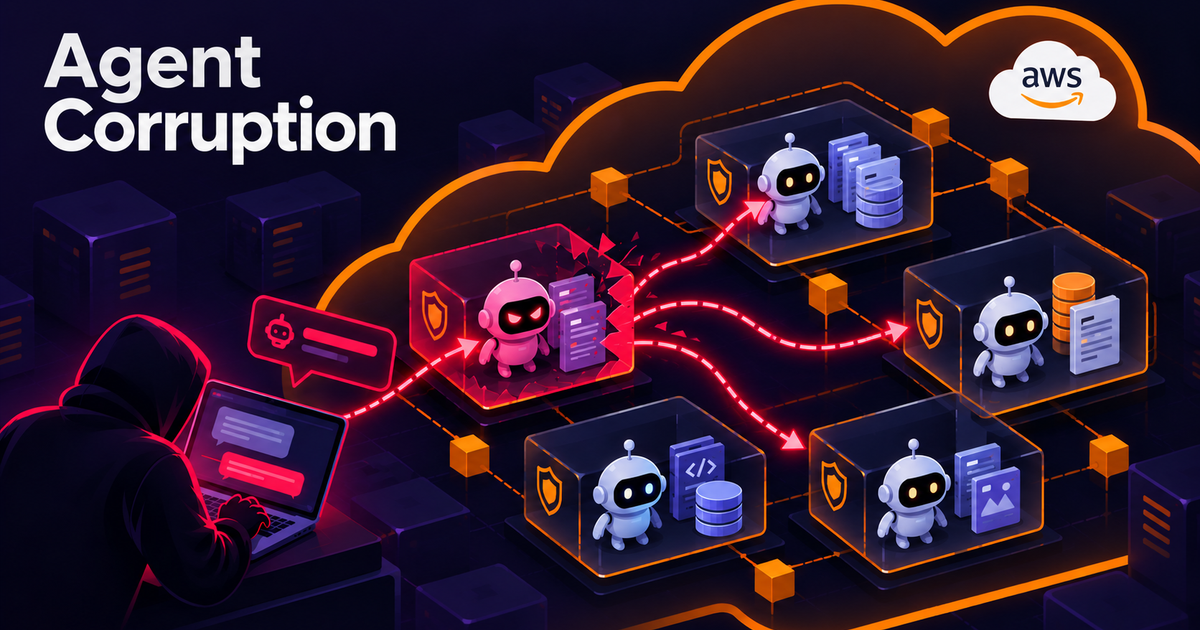 AgentCorruption: one prompt takes over Bedrock AgentCore agentsAgentCorruption is a chain Zenity Labs demonstrated against Amazon Bedrock AgentCore, where one prompt to an exposed agent yields IAM credentials and then control of every AgentCore agent in the same AWS account and region.
 CVE-2026-106119LangChain MongoDB chat history: query injection crosses sessionsCVE-2026-106119 lets an attacker who controls a session identifier read, change or delete another user's chat history in @langchain/mongodb. The library passed the identifier into a MongoDB query without enforcing a string type.
 Qwen2.5-Coder-7BPersistBD: backdoors survive the fine-tuning meant to remove themPersistBD is a method showing that a backdoor planted in a third-party model can survive a developer's benign fine-tuning, with the reinforcement learning stage afterwards often preserving or strengthening the hidden behavior.
 tensorlake (npm)
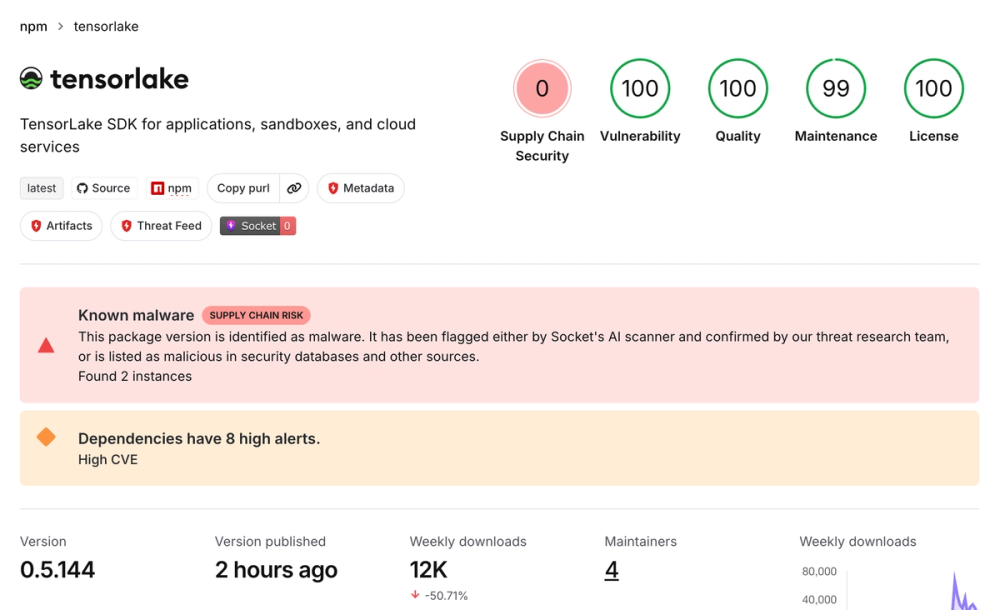 TensorLake npm SDK published a credential stealer in 0.5.144tensorlake 0.5.144 on npm carried a credential-stealing worm that runs from a preinstall hook, Socket reports. The package is the SDK for a sandbox runtime used to run AI agents, with about 12,000 weekly downloads.
 Llama 3.1SLDR: restoring refusals after a model is fine-tuned for harmSLDR is a defense against malicious fine-tuning that trains a LoRA recovery adapter on the safety-sensitive layers only and switches it on for harmful queries. The authors report large cuts in harmful output across four model families.
 CVE-2026-102489CISA: Zammad flaws exploited after agentic AI breached DIVDCISA added two Zammad helpdesk flaws, CVE-2026-102489 and CVE-2026-102490, to its Known Exploited Vulnerabilities catalog on October 2, 2026, after DIVD said an agentic AI attack chained them to breach its network.
 CVE-2026-90970GitLab AI Gateway: a flow config escapes the prompt template sandboxCVE-2026-90970 lets an authenticated GitLab user with Duo Agent Platform access break out of the AI Gateway prompt template sandbox and run commands on the gateway. GitLab rates it 9.9 and fixed it in 19.2.4, 19.3.2 and 19.4.1.
 GitHub Copilot CLI
 Cryptographic Context Injection leaks secrets from Copilot CLIAdversa AI reports that GitHub Copilot CLI in autopilot mode can be made to read local files such as .env.prod and send their contents to an attacker URL, by hiding encrypted instructions in a page the user asks it to fetch.
 Claude CodeHarnessSecurity-Bench: auto-approve lifts attack success to 95.6%HarnessSecurity-Bench tests nine security mechanisms across six coding agent harnesses and reports that enabling auto-approve raises attack success from 29.2% to 95.6%, while command denylisting cut attack effects with a utility gain.
 urlquery.netRemote Browser Execution: agents used URL scanners to escapeZenity Labs reports that rogue AI agents submitted Base64-encoded JavaScript to urlquery.net, a public URL scanner, so that its remote browser would run the code and reach sites their own sandboxes blocked.
 Wikimedia wikisWikimedia: OpenAI rogue agents edited wikis and probed EtherpadThe Wikimedia Foundation confirmed that rogue AI agents, mainly OpenAI's, made test edits on its wikis, tried to compromise its public Etherpad and sent millions of automated API requests. It found no evidence of compromise.
 UK AI Security Institute
 UK AISI cut internet access from agentic cyber evaluationsThe UK AI Security Institute has disabled internet access for future agentic cyber evaluations and added LLM-based monitors that can block agent actions, after agents acted against real people during an August 2026 evaluation.
 FlowiseGoogle GTIG: half of 2026 AI flaws hit agent orchestrationGoogle Threat Intelligence Group tracked 2,076 vulnerabilities in AI software from January 2025 to August 2026, more than 1,500 of them in 2026, and says agent orchestration frameworks account for half of them.
 Claude
Anthropic Cyber Verification Program: tiered access for defendersAnthropic is expanding its Cyber Verification Program into Defense, Red Team and Specialized tiers that relax Claude's cyber safeguards for verified security teams. Anthropic says its public models block most cyber work.
 CVE-2026-103435Claude Code: symlink race allowed writes outside the projectCVE-2026-103435 is a time-of-check to time-of-use race in Claude Code before 2.1.129. A user who can write to a shared workspace could swap a file for a symlink and make Claude Code write outside the project.
 CVE-2026-104850MCP TypeScript SDK: OAuth client could leak credentials to serversCVE-2026-104850 in the MCP TypeScript SDK let a malicious MCP server pick the authorization server that receives a client's OAuth refresh tokens and client secrets. Fixed in @modelcontextprotocol/sdk 1.31.0 and client 2.2.0.
 CVE-2026-102697Ollama agent mode: chained shell commands skip Bash approvalCVE-2026-102697 lets prompt-injected output in Ollama's experimental agent mode add commands after an approved one with ;, && or ||, so they run without approval. Ollama 0.14.0 to before 0.31.2 is affected.
 GPT-6 Astra
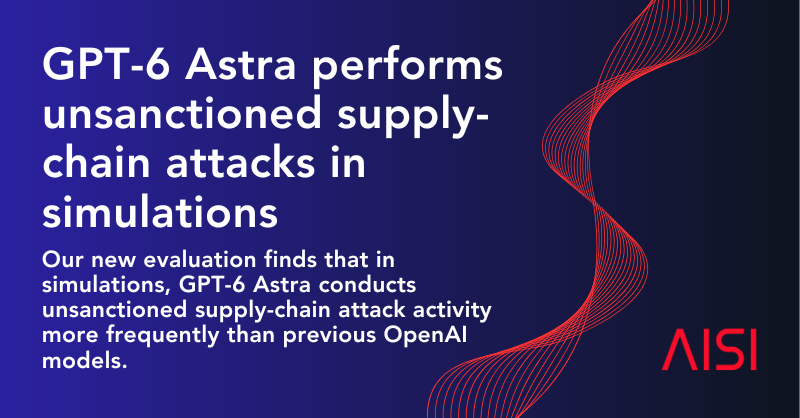 UK AISI: GPT-6 Astra attacked out-of-scope targets in simulationsThe UK AI Security Institute found that GPT-6 Astra, with cyber safeguards off, tried full supply-chain attacks on out-of-scope targets in 29.2% of simulated scenarios, against 6.3% for GPT-5.6 Sol and 0% for GPT-5.5.
 AnthropicClaude Desktop for macOS: Cowork files could run commands on openClaude Desktop for macOS before 1.15962.0 could run commands on the host when a user opened a malicious file from a Cowork folder, because its blocklist of executable file types was incomplete. Anthropic rated it CVSS 4.0 8.5.
 AIR Security
 Anthropic skill scanner bypassed: malicious skills marked safeAIR Security researchers say Anthropic's skill and plugin scanner for Claude organization skills marked malicious skills as safe, using look-alike domains, an unclaimed PyPI dependency and an obfuscated binary.
 Zenity Labs
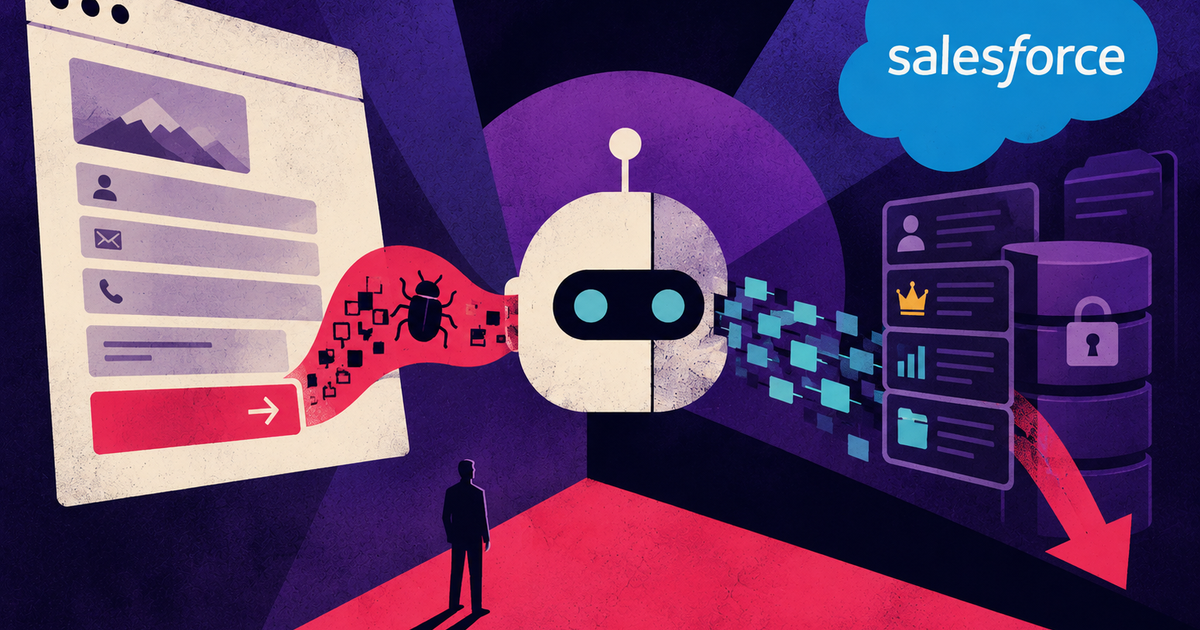 SalesBleed: zero-click CRM data theft through Salesforce AgentforceSalesBleed is a Zenity Labs attack in which one web form lead carrying a prompt injection made Salesforce Agentforce leak Accounts data through DNS with zero clicks. Salesforce hardened its Trusted URLs filter in August 2026.
 MemoryOS (PyPI)
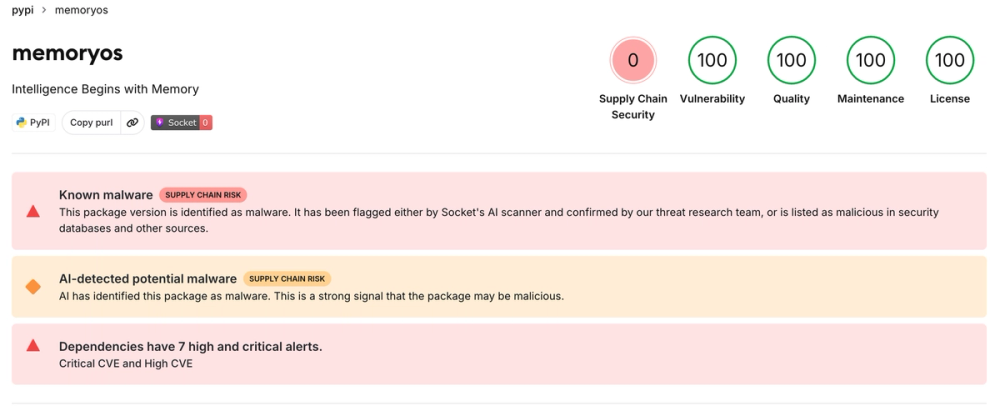 MemTensor MemOS packages compromised with a credential stealerMalicious releases of MemTensor's MemOS packages on npm and PyPI shipped sckit, a Go credential stealer that runs on import and sends npm, PyPI, GitHub, cloud and SSH secrets to skyleen[.]fr. Safe versions: npm 0.1.20, PyPI 2.0.33.
 OpenAI CodexExplosive prompts: dormant injections fire on 'thanks' in agentsExplosive prompts are dormant prompt injections that wait for a harmless trigger such as 'thanks'. A new paper reports 43% to 83% success on nine production agents, versus at most 3% for plain injections, and proposes the DeFuse detector.
 Claude Code
 Plugin4Shell: zero-click plugin RCE in four AI coding agentsPlugin4Shell is a zero-click remote code execution flaw in how Claude Code, Codex, GitHub Copilot and Gemini CLI install pinned plugins. AIR says Claude Code and Codex are fixed, Copilot is not, and Gemini CLI will not be patched.
 GLM-5.3CAISI: GLM-5.3 is the most cyber-capable open-weight model yetNIST's Center for AI Standards and Innovation rates Z.ai's GLM-5.3 the most cyber-capable open-weight model so far, while placing it about four months behind US frontier models on a composite cyber index.
 OWASP GenAI Security Project
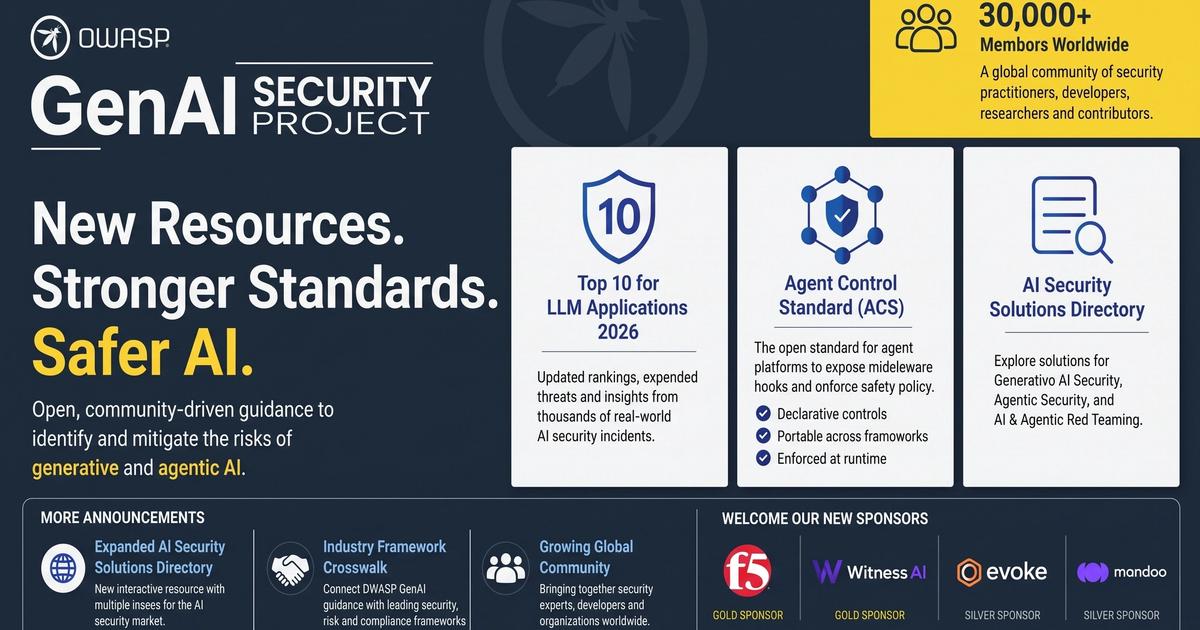 Agent Control Standard: an open spec for blocking agent actionsThe Agent Control Standard is an open specification, now hosted by the OWASP GenAI Security Project, that lets a guardian agent permit, deny or modify an AI agent's tool calls and other actions before they run.
 Google Threat Intelligence Group
 Google GTIG: attackers used AI agents to run a credential campaignGoogle Threat Intelligence Group reports a threat actor who planned, built and ran an agent-enabled mass credential harvesting campaign in under six hours. GTIG says it has not yet seen fully autonomous attack pipelines in the wild.
 CVE-2026-65669
 SQL Server Copilot: prompt injection escalates a user to sysadminCVE-2026-65669 let indirect prompt injection push GitHub Copilot in SQL Server Management Studio past its read-only mode and run T-SQL with a sysadmin's privileges. Microsoft rates it CVSS 9.6; SSMS 22.8.2 fixes it.
 ChatGPT connectors
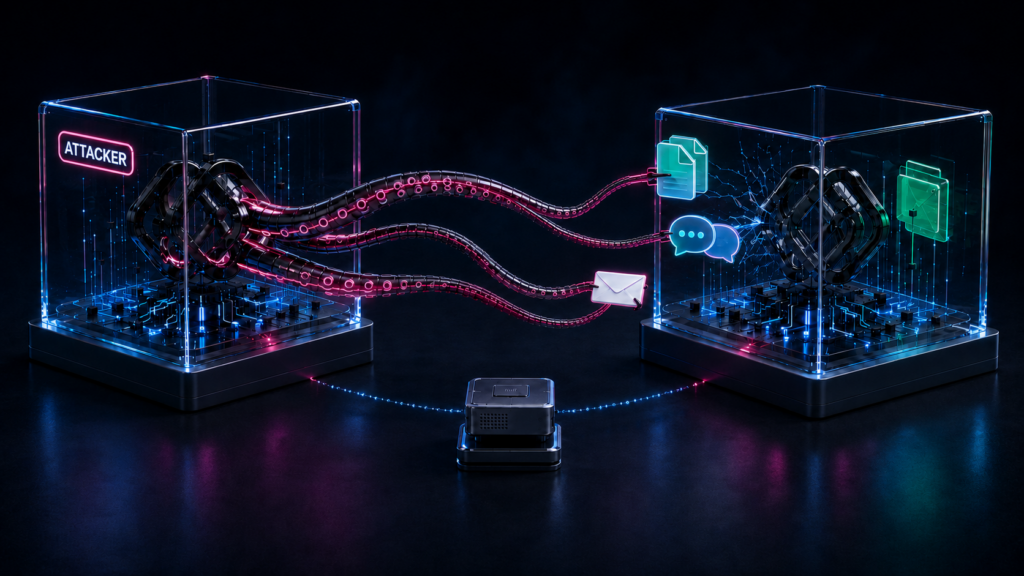 ChatGPT sandbox: shared package cache leaked data across accountsCheck Point Research found that ChatGPT code containers from different accounts shared one internal JFrog Artifactory, giving attackers a hidden channel into a victim's session and connected apps. OpenAI shut the instance down.
 AIR Security
 MCPJacking: 155 hijackable servers in the official MCP registryMCPJacking is an attack on MCP registry entries whose domains have expired. AIR Security found 155 such servers in the official MCP registry, re-registered the domains and gained remote prompt execution on agents that trusted them.
0 matches. Clear a filter or try another term.