Visual Studio Copilot: a trailing dot let the agent rewrite its own config
A trailing period defeated the check on which files Copilot may edit, letting an injected agent point the IDE at a binary it chose.
· Embrace The Red · Research by Johann Rehberger
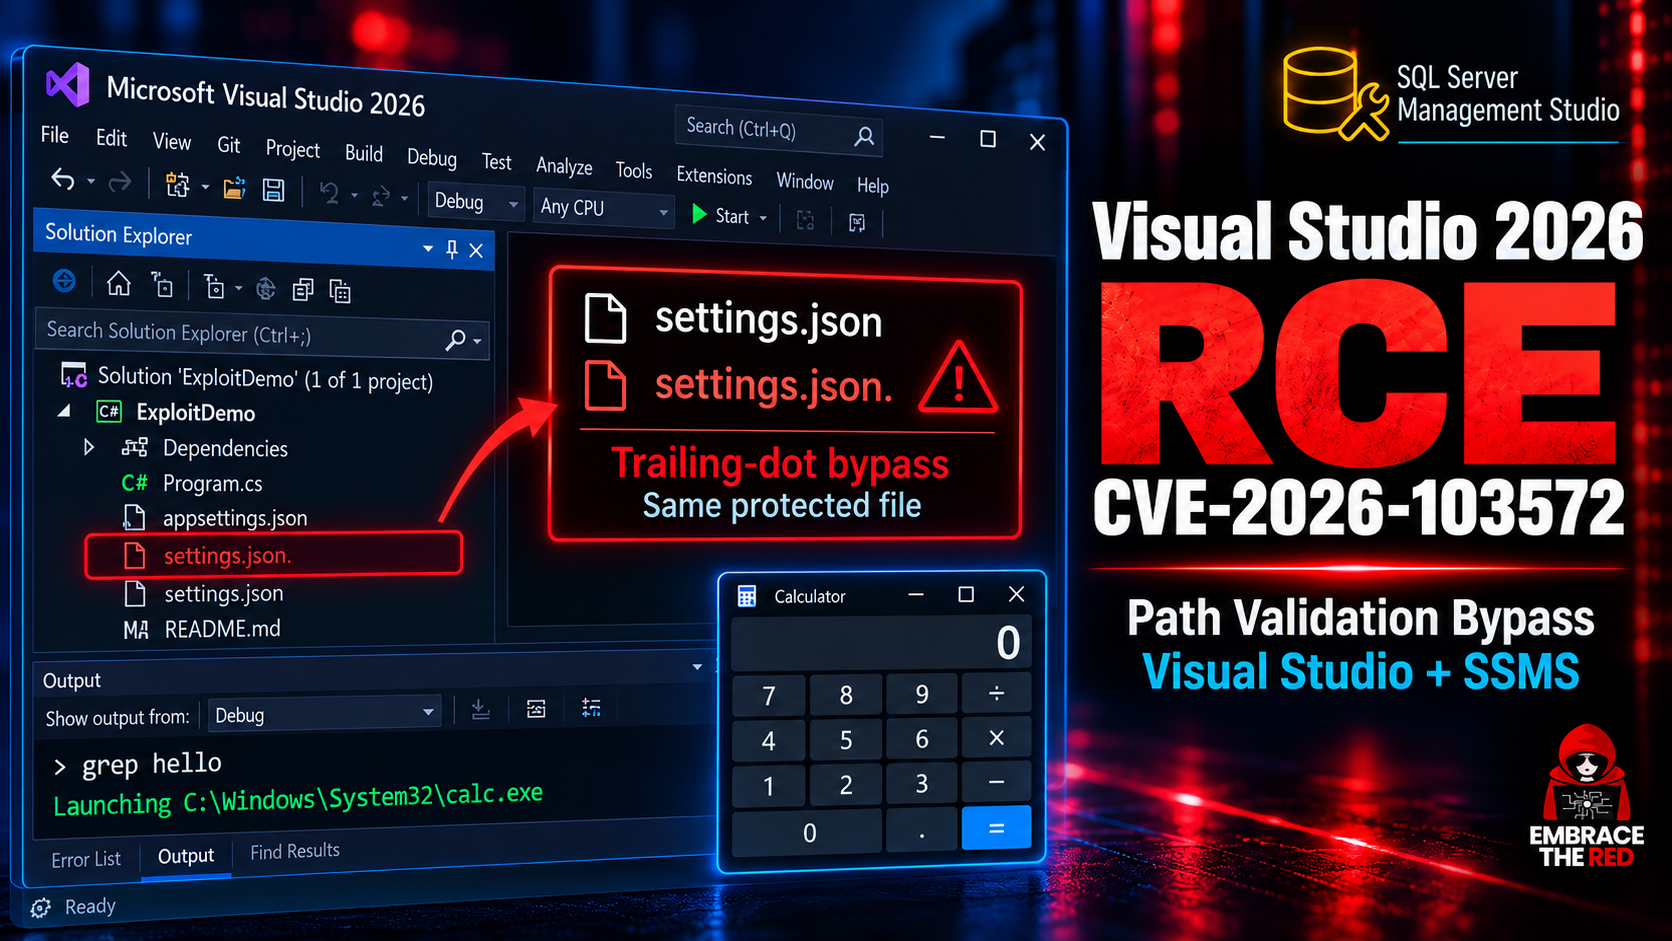
CVE-2026-103572 let GitHub Copilot in Visual Studio and SSMS write to its own MCP and settings files by adding a trailing dot to a blocked path, turning a compromised agent into code execution. Microsoft fixed it on October 13.
- embracethered.comEmbrace The Red Post
- cveawg.mitre.orgCVE Record
- msrc.microsoft.comMSRC Advisory
- +1 sources
01What happened
Microsoft published CVE-2026-103572 on October 13, 2026 and shipped the fix the same day in its October Patch Tuesday release. Johann Rehberger of Embrace The Red reported the path bypass to MSRC on August 4, 2026, Microsoft confirmed it on September 16, and he published his write-up on October 13. Rehberger notes the report earned no bounty.
02How it works
Windows saves a file name that ends in a period without that character, so settings.json and settings.json. are the same file. Copilot's confirmation check, GetEditConfirmationTypeAsync in Microsoft.VisualStudio.Copilot.Core.dll, compared path strings, so .mcp.json. passed while the write landed on .mcp.json. Rehberger chained the write into code execution two ways: adding an attacker-controlled MCP server that the IDE then launches, and overwriting the ripgrep path in settings.VisualStudio.json so a binary of his choice runs during a search. His proof of concept started calc.exe.
03Who is affected
Developers running Copilot in Visual Studio 2022 or Visual Studio 2026 are exposed, in the version ranges Microsoft lists in the table below. Rehberger reports that SQL Server Management Studio is affected too, because it shares the Copilot code with Visual Studio. Exploitation needs the agent to be injected or misaligned first, which is the threat model his post argues security controls must survive.
04What to do
Install the October 2026 Patch Tuesday updates for Visual Studio, and for SQL Server Management Studio alongside them. Rehberger's advice is to patch both. Because both attack chains work by writing agent configuration that the IDE later executes, review a project's .mcp.json and Visual Studio settings files for MCP servers or tool paths nobody added.
Questions people ask
- Which Visual Studio versions fix CVE-2026-103572?
- Visual Studio 2022 version 17.14.42 and Visual Studio 2026 version 18.10.4 fix CVE-2026-103572, according to Microsoft's CVE record. Earlier builds in the 17.14 and 18.10 lines are listed as affected. Johann Rehberger also reports that SQL Server Management Studio shares the vulnerable Copilot code, so SSMS installations deserve an update in the same pass.
- Is SQL Server Management Studio affected by CVE-2026-103572?
- SQL Server Management Studio is affected, according to Johann Rehberger, who found the flaw and notes that SSMS shares Copilot code with Visual Studio. Microsoft's CVE title names both Visual Studio Tools for Applications and SQL Server Management Studio, though its machine-readable affected list shows only Visual Studio 2022 and Visual Studio 2026 builds. Administrators should patch SSMS as well.
- How does CVE-2026-103572 differ from the earlier SQL Copilot sysadmin flaw?
- CVE-2026-103572 is a file path validation bypass that lets Copilot write its own MCP and settings files, which leads to code execution on the developer's machine. The earlier flaw Rehberger disclosed, CVE-2026-65669, was a read-only bypass inside SQL Server Management Studio that escalated a user to sysadmin in the database. Different mechanism, different target, same researcher.
- How can I tell whether an agent changed my MCP configuration?
- Open the project's .mcp.json and the Visual Studio settings files and look for MCP servers or tool paths nobody added. Rehberger's two attack chains work by registering an attacker-controlled MCP server that the IDE then launches, or by repointing the ripgrep path so a chosen binary runs during a search. Entries naming unfamiliar commands deserve scrutiny.
Sources 4 links, all fetched
- 1embracethered.comEmbrace The Red Post
- 2cveawg.mitre.orgCVE Record
- 3msrc.microsoft.comMSRC Advisory
- 4learn.microsoft.comWindows Trailing Dots