MemoryOS (PyPI)
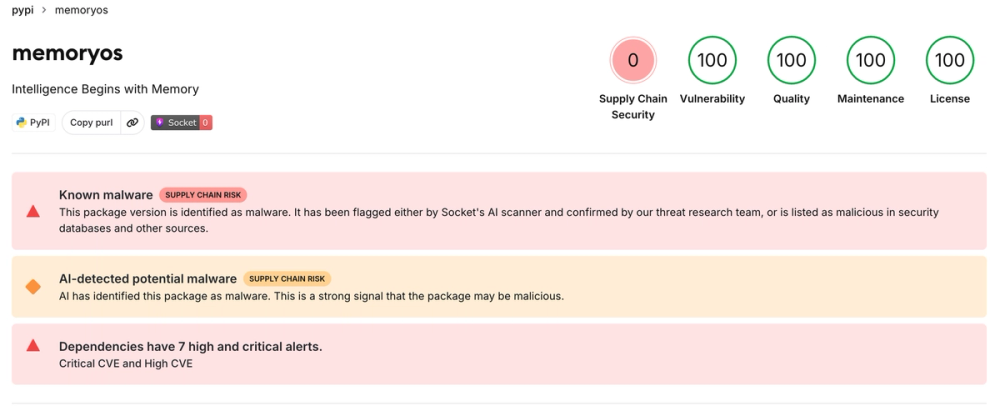
HIGHSupply chain
HIGHSupply chain
MemTensor MemOS packages compromised with a credential stealer
Poisoned releases of an LLM memory framework stole developer and cloud credentials the moment they loaded.
- Affects
- @memtensor/memos-cloud-openclaw-plugin, MemoryOS (PyPI), MemOS
- Malicious npm
- @memtensor/memos-cloud-openclaw-plugin 0.1.21, 0.1.23, 0.1.25
- Malicious PyPI
- MemoryOS 2.0.34
- Safe versions
- npm 0.1.20 or earlier; PyPI 2.0.33 or earlier
- Credit
- Karlo Zanki
30-day exposure by ecosystem
hover a day for its storiesCoding agents5 events
MCP & plugins4 events
Packages & models6 events
Assistants & apps6 events
Labs & evals3 events
High / criticalMediumLow / info
Incident feed
17 of 17 · newest first- Claude
INFOLab safetyAnthropicAnthropic Cyber Verification Program: tiered access for defenders
- CVE-2026-103435MEDVulnerabilityAnthropicCVE-2026-103435Claude Code: symlink race allowed writes outside the project
- CVE-2026-104850HIGHVulnerabilityModel Context ProtocolCVE-2026-104850MCP TypeScript SDK: OAuth client could leak credentials to servers
- CVE-2026-102697HIGHVulnerabilityVulnCheckCVE-2026-102697Ollama agent mode: chained shell commands skip Bash approval
- GPT-6 Astra
 INFOBenchmarkUK AI Security InstituteUK AISI: GPT-6 Astra attacked out-of-scope targets in simulations
- AnthropicHIGHVulnerabilityAnthropicClaude Desktop for macOS: Cowork files could run commands on open
- AIR Security
 MEDAttackAIR SecurityAnthropic skill scanner bypassed: malicious skills marked safe
- Zenity Labs
 MEDAttackZenity LabsSalesBleed: zero-click CRM data theft through Salesforce Agentforce
- MemoryOS (PyPI)HIGHSupply chainSocketMemTensor MemOS packages compromised with a credential stealer
- OpenAI CodexMEDResearcharXivExplosive prompts: dormant injections fire on 'thanks' in agents
- Claude Code
 HIGHVulnerabilityAIR SecurityPlugin4Shell: zero-click plugin RCE in four AI coding agents
- GLM-5.3INFOBenchmarkNIST CAISICAISI: GLM-5.3 is the most cyber-capable open-weight model yet
- OWASP GenAI Security Project
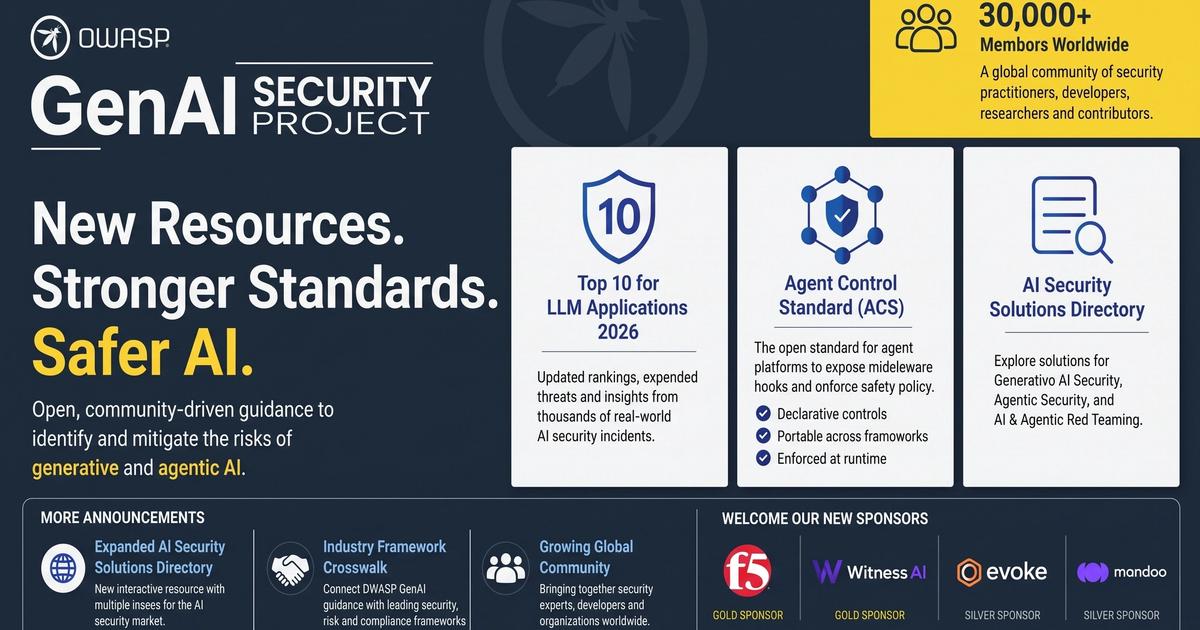 INFOToolOWASP GenAI Security ProjectAgent Control Standard: an open spec for blocking agent actions
- Google Threat Intelligence Group
 INFOIncidentGoogle Threat Intelligence GroupGoogle GTIG: attackers used AI agents to run a credential campaign
- CVE-2026-65669
 HIGHVulnerabilityEmbrace The RedCVE-2026-65669SQL Server Copilot: prompt injection escalates a user to sysadmin
- ChatGPT connectors
 LOWVulnerabilityCheck Point ResearchChatGPT sandbox: shared package cache leaked data across accounts
- AIR Security
 HIGHSupply chainAIR SecurityMCPJacking: 155 hijackable servers in the official MCP registry