Plugin4Shell: zero-click plugin RCE in four AI coding agents
A git branch named after a commit hash lets an attacker swap a pinned, reviewed plugin for malicious code during auto-update.
· AIR Security · Research by Or Nevo, Dor Granat, Niv Hoffman
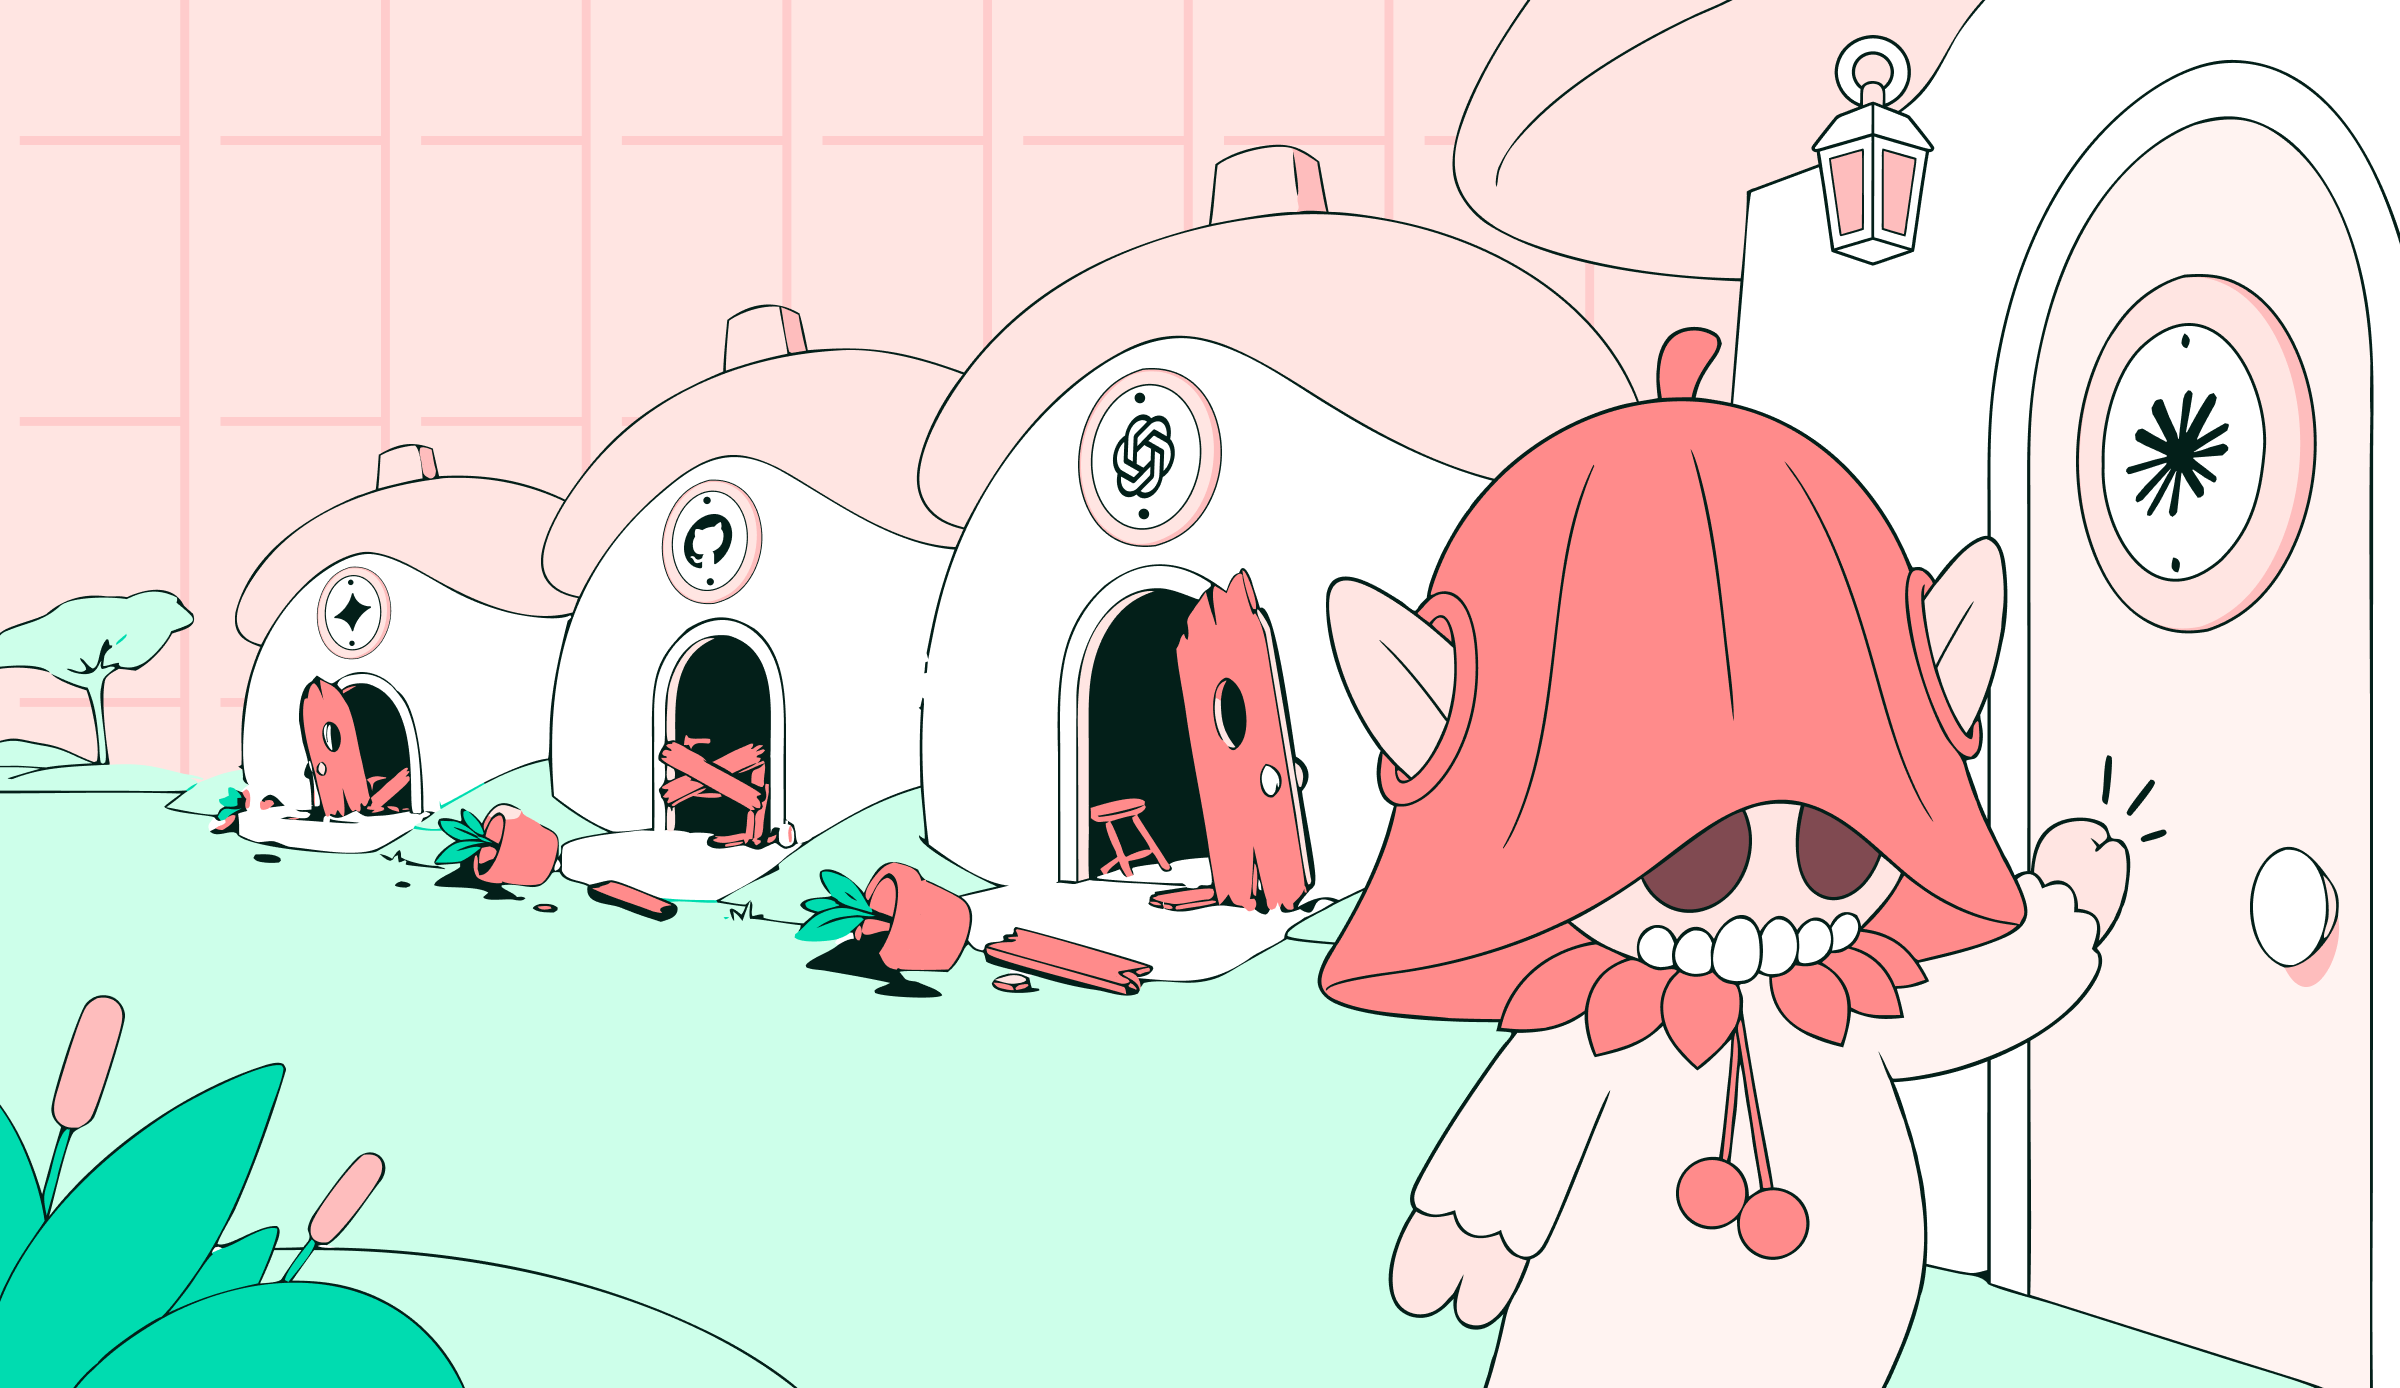
Plugin4Shell is a zero-click remote code execution flaw in how Claude Code, Codex, GitHub Copilot and Gemini CLI install pinned plugins. AIR says Claude Code and Codex are fixed, Copilot is not, and Gemini CLI will not be patched.
01What happened
AIR Security researchers found that four major AI coding agents can silently install a malicious plugin even when the marketplace pins it to a specific commit. They found the issue in May 2026, disclosed it to all four vendors in June, and published Plugin4Shell on September 17, 2026.
02How it works
An attacker publishes a harmless plugin that passes review. When the marketplace later re-pins the plugin to a new commit, the attacker creates a branch whose name is that exact commit hash and points it at malicious code. Git prefers the branch name over the commit id, so the agent's background auto-update checks out the attacker's code, and none of the agents checked that the checkout landed on the pinned commit. Gemini CLI falls to a variant that uses a default branch named FETCH_HEAD.
03Who is affected
Users of Claude Code, Codex, GitHub Copilot and Gemini CLI who install plugins from a marketplace. AIR reports Claude Code fixed in 2.1.179 and Codex in 0.146.0, Copilot without a fix, and Gemini CLI deprecated by Google without a patch.
04What to do
Update Claude Code to 2.1.179 or later and Codex to 0.146.0 or later. Audit plugins installed in Copilot, and move off Gemini CLI, which Google advises replacing with Antigravity.
Questions people ask
- Is Claude Code patched against Plugin4Shell?
- Claude Code is patched against Plugin4Shell, according to AIR Security, which says Anthropic confirmed the fix on June 17, 2026 in Claude Code 2.1.179. Users who run an older Claude Code build and install plugins from a marketplace should update to 2.1.179 or later, because AIR says updating the agent is the only complete mitigation.
- Is GitHub Copilot still vulnerable to Plugin4Shell?
- GitHub Copilot had no fix for Plugin4Shell when AIR Security published its research on September 17, 2026. AIR states that Microsoft has not shipped a fix, so Copilot users have no patch. Until a fix ships, teams using Copilot plugins should review which plugins are installed and limit plugin sources to ones they trust and monitor.
- What should Gemini CLI users do about Plugin4Shell?
- Gemini CLI users should plan to migrate, because AIR Security reports that Google confirmed on August 4, 2026 that it will not patch Plugin4Shell and has deprecated Gemini CLI. Google advises moving to Antigravity. Gemini CLI is hit by a variant in which a repository default branch named FETCH_HEAD resolves instead of the fetched commit.
- Can a plugin marketplace block Plugin4Shell on its own?
- A plugin marketplace cannot fully block Plugin4Shell, according to AIR Security, because the missing check sits inside the coding agent. Each agent checks out the pinned commit but never confirms that the code on disk matches it. AIR says the fix has to ship in the agent, which is why updating Claude Code and Codex matters.
Sources 3 links, all fetched
- 1air.securityAIR Write-up
- 2github.comCodex 0.146.0 Release
- 3air.securityAIR Follow-up Framework