ChatGPT sandbox: shared package cache leaked data across accounts
Item properties on a shared package cache worked as a two-way message board between separate ChatGPT accounts.
· Check Point Research · Research by Alexey Bukhteyev
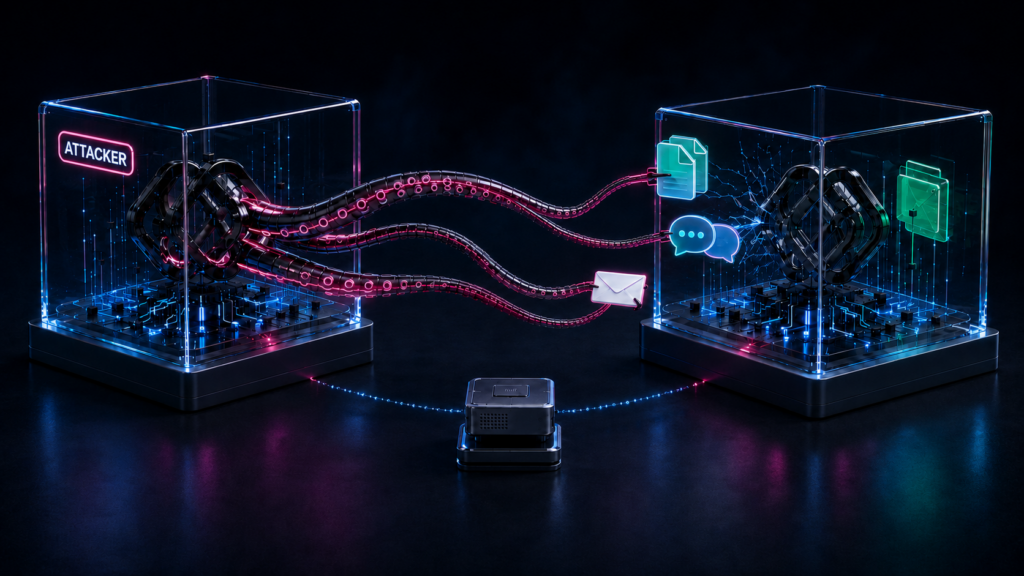
Check Point Research found that ChatGPT code containers from different accounts shared one internal JFrog Artifactory, giving attackers a hidden channel into a victim's session and connected apps. OpenAI shut the instance down.
01What happened
Check Point Research published findings on September 8, 2026 about a cross-account channel in ChatGPT's code execution sandbox, found in June 2026. OpenAI confirmed that the internal Artifactory instance had been decommissioned, which closed the channel.
02How it works
Code containers from different ChatGPT accounts could reach the same internal JFrog Artifactory and read and write item properties on cached files without isolation. An attacker who gets instructions into a victim's session, through a malicious prompt, a shared conversation or a custom GPT, can have the victim's session answer the visible request while also running hidden tasks. Results, such as data pulled through connected apps like Gmail, then travel back through the shared properties.
03Who is affected
ChatGPT users with code execution and connected apps such as Gmail, Google Drive, Microsoft Teams or GitHub, before OpenAI decommissioned the shared instance. Check Point does not report exploitation in the wild.
04What to do
No user action is needed for this channel. As a general rule, be careful with shared conversations and custom GPTs from unknown authors when connectors to sensitive accounts are on.
Sources 2 links, all fetched
- 1research.checkpoint.comCheck Point Research
- 2csoonline.comCSO Online Coverage